The 4-Layer AI Security Stack
Protection across every layer of your AI infrastructure, from agents and LLMs to MCP integrations and ML pipelines.
Behavior Monitoring
Real-time tracking of agent actions, tool calls, and decision patterns to detect anomalous behavior.
Permission Boundaries
Fine-grained permission policies that limit what each agent can access, execute, and modify.
Guardrails
Input/output guardrails that enforce safety constraints and prevent harmful or off-policy responses.
Multi-Agent Orchestration Security
Secure communication channels between agents with trust verification and delegation controls.
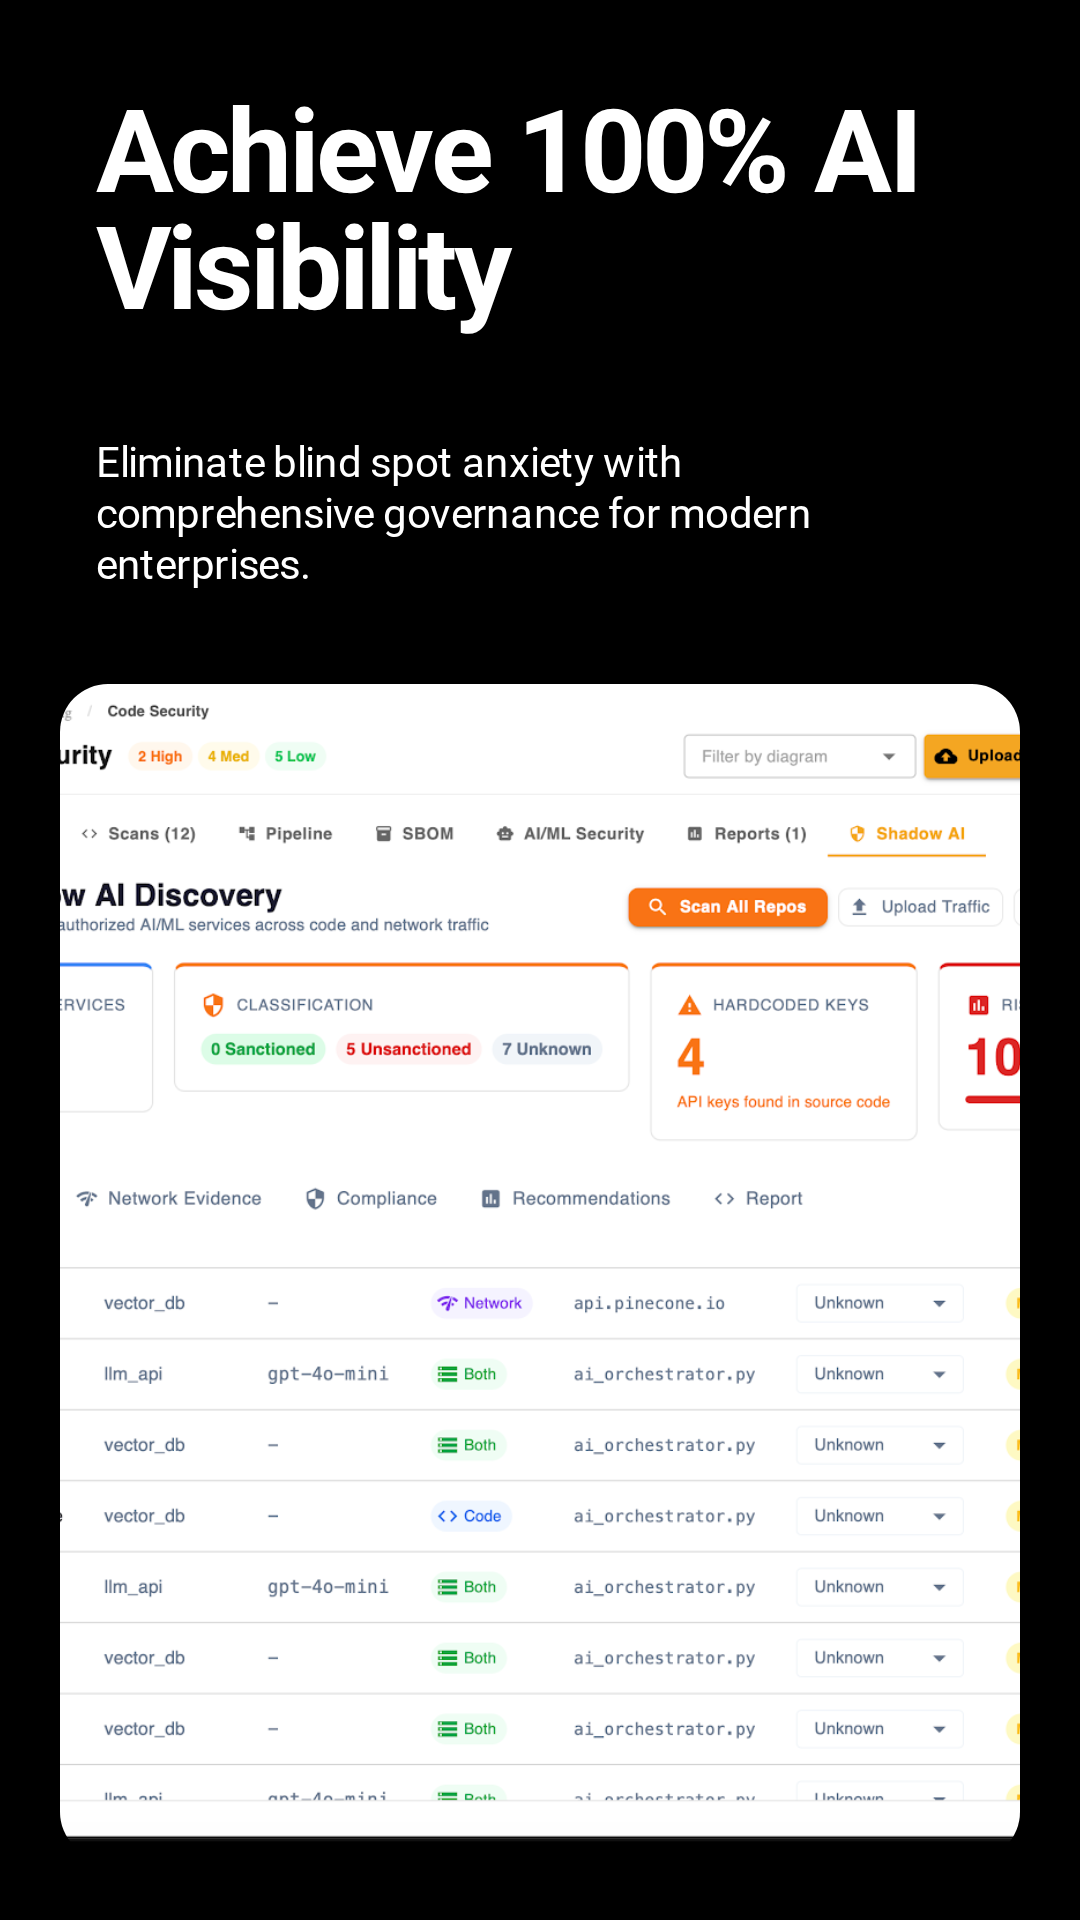
Shadow AI Discovery
Auto-discover ungoverned AI across your enterprise. Employees use dozens of AI tools without security team visibility. Aristiun finds most of them, classifies the risk, and enforces your policies.
Continuous Discovery
Automatically detect AI tools, APIs, and models being used across your organization, including unsanctioned deployments.
Risk Classification
Classify discovered AI by risk level based on data access, model capabilities, deployment context, and regulatory exposure.
Usage Analytics
Full visibility into who is using which AI, how often, with what data, and for what purpose.
Policy Enforcement
Enforce organizational AI policies automatically. Block unapproved models, require approval workflows, and alert on violations.
AI Compliance Frameworks
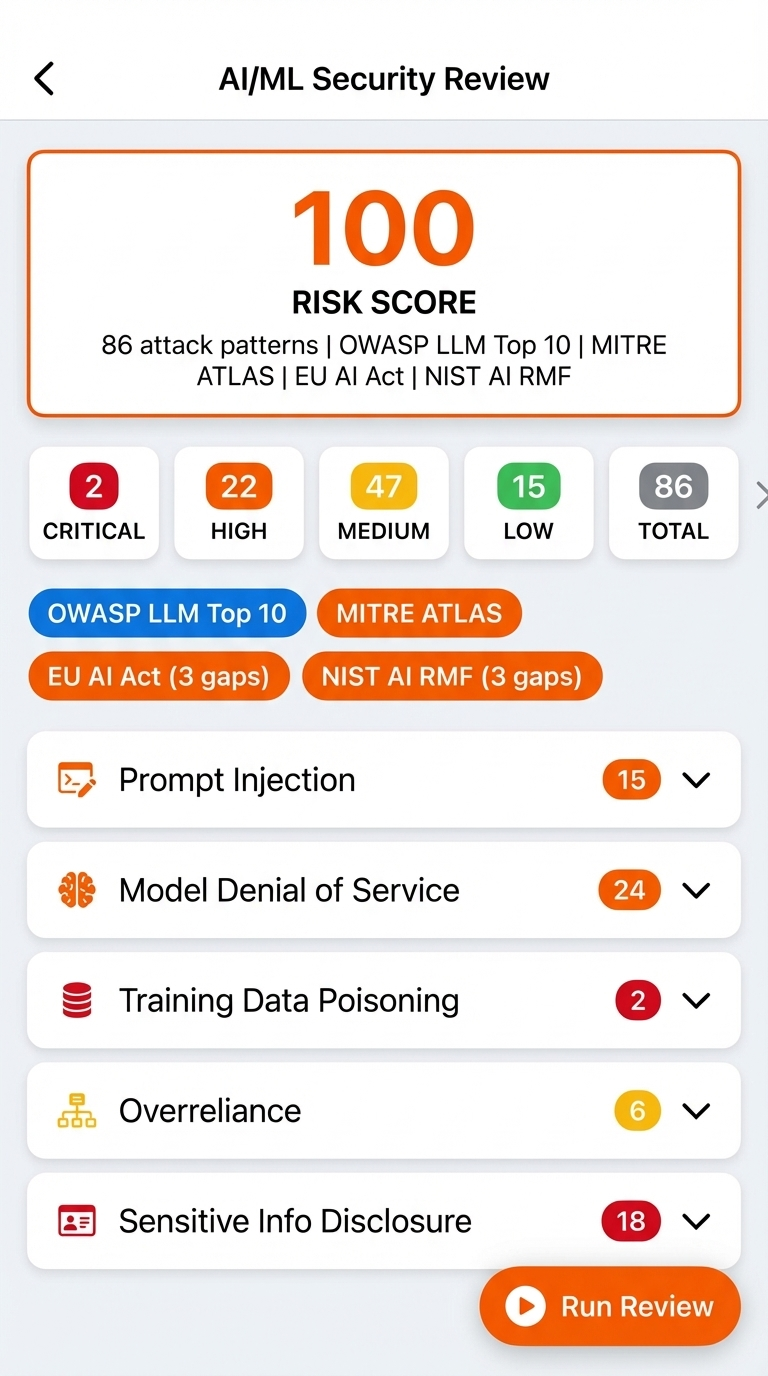
Map your AI security posture to the world's leading AI governance frameworks. Automated evidence collection and continuous compliance monitoring.
EU AI Act
42 controlsFull compliance mapping for high-risk AI systems including risk assessment, transparency obligations, and human oversight requirements.
NIST AI RMF
72 subcategoriesMap, Measure, Manage, and Govern. Full alignment with the NIST AI Risk Management Framework core functions.
ISO 42001
38 controlsAI management system certification support with automated evidence collection and continuous compliance monitoring.
OWASP Top 10 for LLMs
10 risk categoriesProtection against all OWASP LLM risks including prompt injection, insecure output handling, and model theft.
Prompt Injection & AI Attack Prevention
Understand the attack vectors targeting your AI systems and how Aristiun prevents each one with layered defenses.
Direct Prompt Injection
Malicious instructions embedded directly in user input to override system prompts and safety guidelines.
Multi-layer input sanitization, instruction hierarchy enforcement, and canary token detection.
Indirect Prompt Injection
Hidden instructions in external data sources (web pages, documents, emails) that get processed by the LLM.
Data source isolation, content scanning before ingestion, and instruction-data separation boundaries.
Jailbreaking
Techniques to bypass model safety training using role-play, encoding tricks, or multi-turn conversation manipulation.
Output classifiers, behavioral pattern detection, and dynamic guardrail adaptation.
Data Extraction
Probing the model to extract training data, system prompts, API keys, or other sensitive information.
Output filtering, membership inference detection, and differential privacy enforcement.
Model Manipulation
Adversarial inputs designed to produce incorrect predictions, bypass classifiers, or cause model misbehavior.
Adversarial input detection, ensemble verification, and confidence threshold enforcement.
AI Supply Chain Attack
Compromised model weights, poisoned fine-tuning data, or malicious tool packages in the AI development pipeline.
Cryptographic model signing, dependency scanning, and provenance verification across the supply chain.
AI Risk Dashboard
Complete visibility into your AI security posture. Monitor every model, agent, and tool across your enterprise from one dashboard.
Model Inventory
Complete catalog of all AI models in use, both approved and shadow. Track model versions, owners, and deployment locations.
Risk Scores
Dynamic risk scoring for every AI asset based on vulnerability exposure, data sensitivity, and compliance gaps.
Compliance Status
Real-time compliance posture across EU AI Act, NIST AI RMF, ISO 42001, and OWASP Top 10 for LLMs.
Usage Metrics
Token consumption, API call volumes, user adoption rates, and cost analytics across all AI deployments.
Integrates With Your AI Stack
Native integrations with the leading AI platforms, frameworks, and orchestration tools.
Frequently Asked Questions
Everything you need to know about AI security, prompt injection prevention, and AI compliance.
AI security covers the practices, tools, and policies that protect AI systems, including LLMs, agents, and ML pipelines, from adversarial attacks, data breaches, and misuse. It spans the entire AI lifecycle: training data security, inference monitoring, prompt injection prevention, model access controls, output filtering, and compliance with regulations like the EU AI Act and NIST AI RMF.
AI Security Inside the Unified Workbench
AI security is built into Aristiun's unified workbench alongside your digital twin, threat models, and compliance posture. Discover shadow AI, validate AI-specific threats against actual agent code and MCP configurations, and auto-map findings to EU AI Act, NIST AI RMF, and ISO 42001 controls. All from one workspace.
Powered by Ayurak AI
AI Security Platform Demo
Discover shadow AI, classify model risks, and enforce governance policies across your organization.
Explore Related Solutions
Automated Threat Modeling
AI-powered STRIDE, PASTA, and LINDDUN analysis for your architecture
Learn moreCode Security
Architecture-aware SAST, DAST, and SCA scanning with remediation playbooks
Learn moreAI Governance
Enterprise AI governance policies and risk management frameworks
Learn moreCompliance Automation
Map controls across 340+ frameworks with continuous evidence collection
Learn moreAristiun's AI security platform is powered by Ayurak AI — intelligence that protects what matters.