NIST Risk Assessment Automation
Automate your NIST 800-53, NIST CSF 2.0, and NIST RMF assessments with AI-powered control mapping, continuous monitoring, and audit-ready reporting. Most customers go from kickoff to audit-ready in weeks, not months.
Every NIST Framework. One Platform.
Aristiun's NIST CSF assessment platform covers the full spectrum of NIST cybersecurity framework automation, from foundational controls to AI-specific risk management.
NIST CSF 2.0
CSF 2.0 organizes outcomes across six functions: Govern, Identify, Protect, Detect, Respond, and Recover. It gives you a shared language for managing cybersecurity risk across the entire organization.
106 Categories & SubcategoriesNIST 800-53 Rev 5
The largest federal catalog of security and privacy controls. Rev 5 includes 1,189 controls across 20 families, covering everything from access control and audit to incident response and system protection.
1,189 Controls, 20 FamiliesNIST SP 800-37 RMF
The Risk Management Framework walks you through a seven-step process for building security into the system development lifecycle, starting at categorization and running through continuous monitoring.
7-Step Lifecycle ProcessNIST AI RMF 1.0
The AI Risk Management Framework addresses risks unique to artificial intelligence systems, covering governance, mapping, measuring, and managing AI risk across the entire AI lifecycle.
4 Functions, 19 CategoriesNIST 800-171 Rev 3
Protects Controlled Unclassified Information (CUI) in non-federal systems. Required for defense contractors and CMMC compliance, covering 110 security requirements derived from NIST 800-53.
110 Security RequirementsNIST Privacy Framework
A voluntary framework for managing privacy risk. Maps directly to the Cybersecurity Framework and supports compliance with GDPR, CCPA, and other global privacy regulations.
100+ Privacy ControlsFrom Architecture to Automated NIST Compliance in 5 Steps
Here's how Aristiun's NIST risk assessment automation platform turns a multi-month assessment into a continuous compliance workflow, powered by Ayurak AI.
Upload Architecture
Import your infrastructure diagrams, cloud configurations, or code repositories. Our platform auto-discovers assets, data flows, and trust boundaries across your environment.
Auto-Map NIST Controls
Ayurak AI maps your architecture components to relevant NIST 800-53, NIST CSF, and NIST RMF controls. It identifies which of the 1,189+ controls actually apply to your specific environment.
Gap Analysis
The platform performs an automated gap analysis comparing your current security posture against applicable NIST requirements, highlighting missing controls, partial implementations, and policy gaps.
Remediation Plans
Receive prioritized, actionable remediation plans with implementation guidance, effort estimates, and code-level fixes aligned to NIST control requirements.
Continuous Monitoring
Maintain ongoing NIST compliance with continuous monitoring that detects configuration drift, new vulnerabilities, and control failures. Your assessment stays current around the clock.
Enterprise-Grade NIST Assessment Features
Everything you need for automated NIST compliance, from initial assessment through continuous NIST monitoring and audit preparation.
Automated Control Mapping
Maps your infrastructure to NIST 800-53, CSF 2.0, and RMF controls using AI. Most teams tell us this cuts weeks of manual spreadsheet work. 94% automation accuracy based on customer benchmarks.
Continuous Compliance Monitoring
Real-time monitoring of your NIST compliance posture with automated alerts when configurations drift from established control baselines.
Gap Analysis & Remediation
Automated identification of control gaps with prioritized remediation plans, effort estimates, and implementation guidance aligned to NIST requirements.
Cross-Framework Mapping
Map NIST controls bidirectionally to SOC 2, ISO 27001, HIPAA, FedRAMP, CMMC, PCI DSS, and 340+ other frameworks to eliminate redundant assessments.
Automated Evidence Collection
Pulls compliance evidence from cloud providers, identity systems, and security tools on an ongoing basis. Always organized and ready for auditor review.
Audit-Ready Reports
Generate assessment reports, POA&Ms, and System Security Plans (SSPs) formatted to NIST standards. One click, done.
Risk Scoring & Quantification
Quantify cyber risk using NIST-aligned scoring methodologies. Translate technical findings into business impact metrics for executive reporting.
Real-Time Dashboards
Executive and technical dashboards showing control implementation status, risk trends, compliance scores, and remediation progress across all NIST frameworks.
Aristiun vs Manual NIST Assessment
See how NIST risk assessment automation compares to traditional manual approaches across every dimension that matters.
NIST Assessment Tool Comparison
How Aristiun's NIST 800-53 compliance tool stacks up against Sprinto, Xacta, and Cyber Sierra for full NIST cybersecurity framework automation.
Connects to Your Entire Stack
Pull evidence automatically from your cloud providers, identity systems, DevOps tools, and security platforms for continuous NIST monitoring.
AWS
Cloud
Microsoft Azure
Cloud
Google Cloud
Cloud
Jira
Workflow
ServiceNow
Workflow
Splunk
SIEM
GitHub
DevOps
Azure DevOps
DevOps
GitLab
DevOps
Okta
Identity
Azure AD
Identity
Terraform
IaC
CrowdStrike
Security
Qualys
Security
Slack
Communication
Microsoft Teams
Communication
NIST Assessment by the Numbers
Measurable results from automated NIST compliance across hundreds of enterprise deployments.
NIST Controls Mapped
Automation Rate
Audit Time Reduction
Frameworks Supported
ROI Payback Period
Continuous Monitoring
NIST Risk Assessment: Frequently Asked Questions
Everything you need to know about NIST based assessment, NIST SP 800-37 risk management, and how to automate NIST cybersecurity framework compliance.
Explore Related Solutions
Powered by the Unified Security Workbench
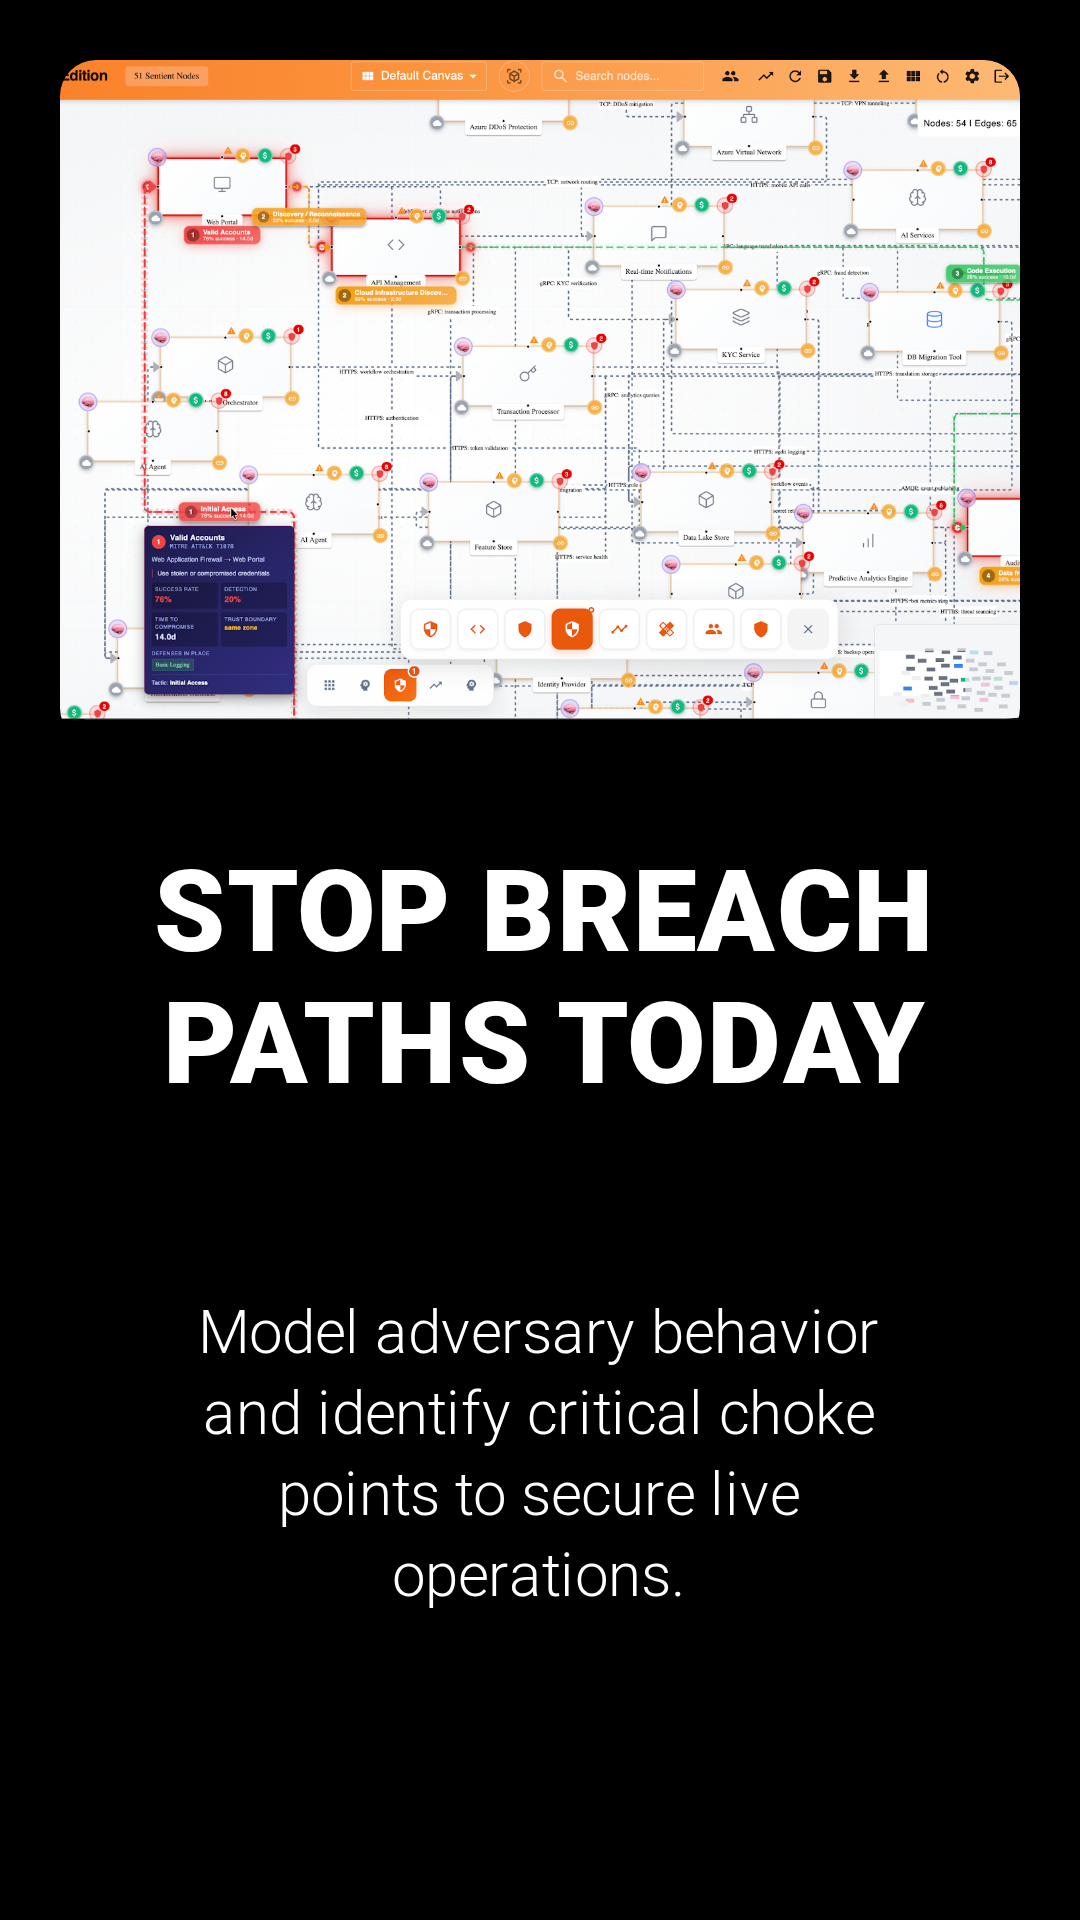
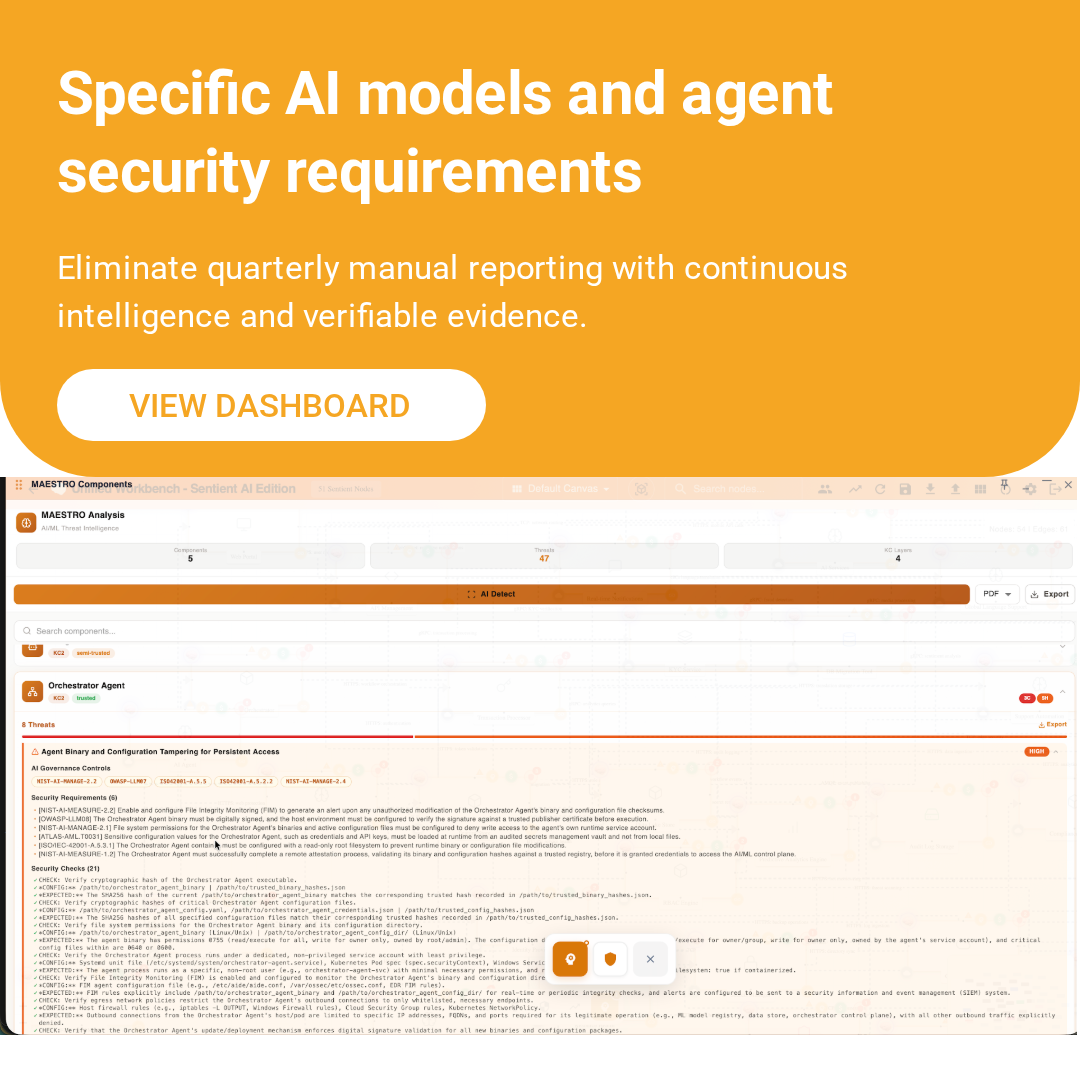
NIST assessments don't exist in isolation. Aristiun's workbench connects your NIST controls to an always-current digital twin of your infrastructure, validates findings against actual code paths, and discovers shadow AI, all in one workspace.
Digital Twin
Always-current model of your infrastructure
Code Validation
Threats traced to code paths
Shadow AI
Ungoverned AI auto-discovered
Cross-Framework
NIST mapped to 340+ standards
Powered by Ayurak AI
NIST Assessment Demo
Watch how Aristiun automates NIST CSF and RMF assessments with real-time risk scoring.
Explore Related Solutions
Automated Threat Modeling
AI-powered STRIDE, PASTA, and LINDDUN analysis for your architecture
Learn moreCompliance Automation
Map controls across 340+ frameworks with continuous evidence collection
Learn moreCompliance Hub
Centralized compliance management across all regulatory frameworks
Learn moreCode Security
Architecture-aware SAST, DAST, and SCA scanning with remediation playbooks
Learn more